
- FortCyber
- Experts
FortCyber experts. Practitioners, not theorists
Auditors, ISMS officers, analysts, lawyers and trainers with experience in companies and the public sector. We know the regulations, and you see everyone’s work on the platform.
Who works for your organisation
Each role has a clear remit and answers to you. You see everyone’s work on the platform.
Security manager
Your dedicated contact. Coordinates the team’s work, keeps track of deadlines and reports to management.
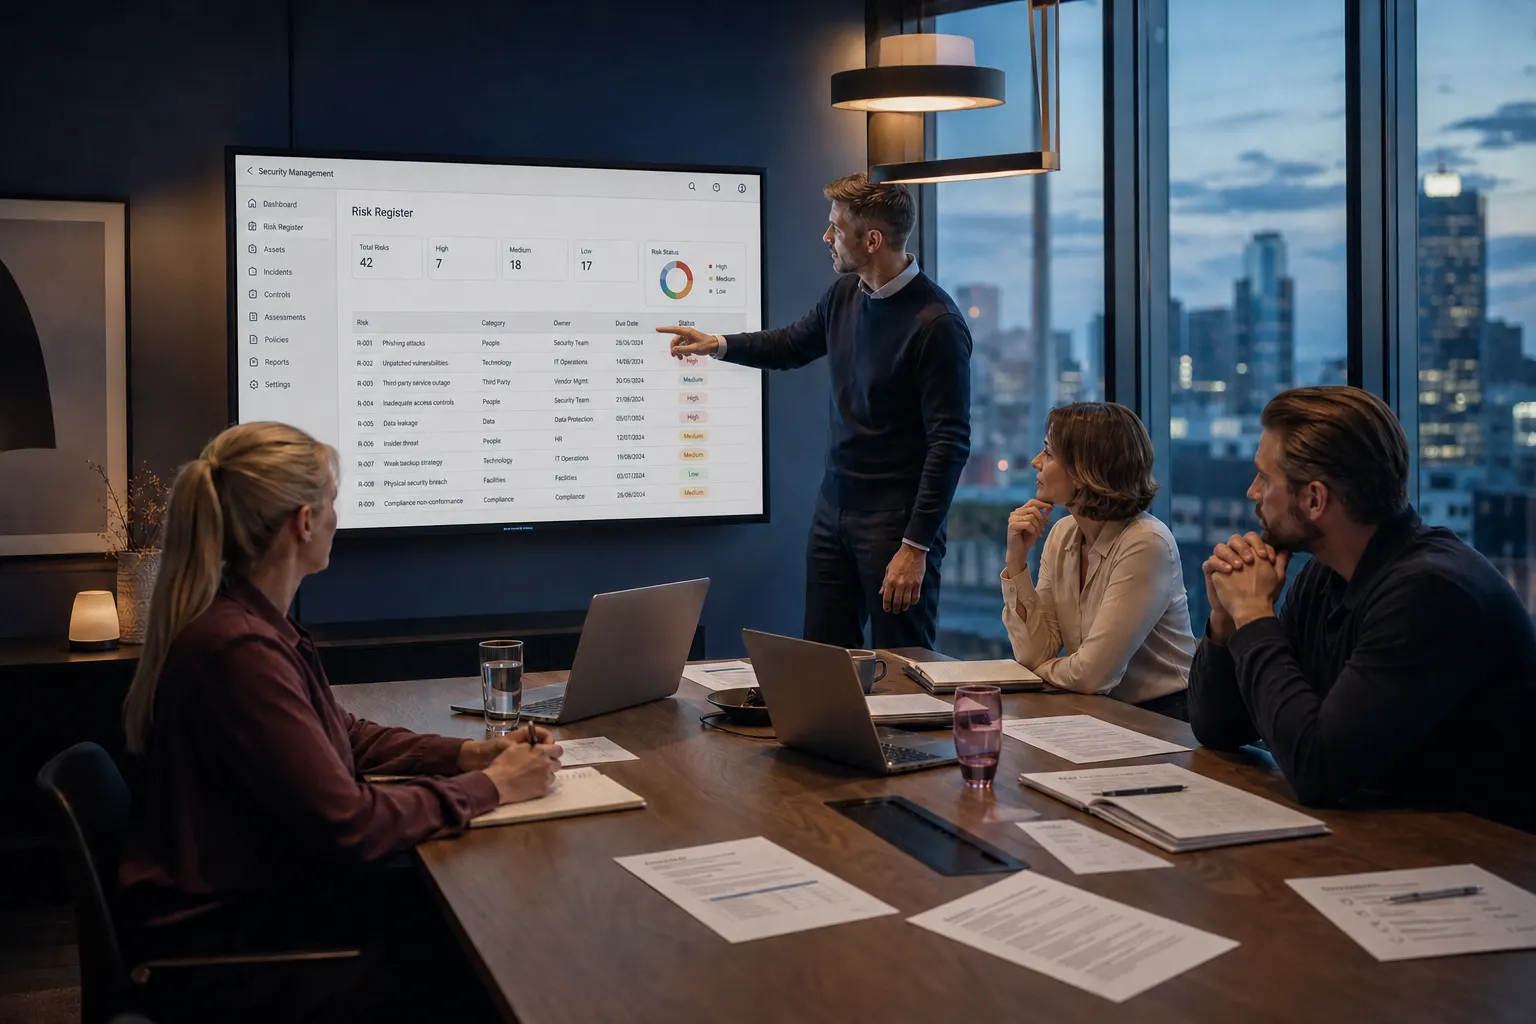
On the platform: management dashboard, decisions to approve and reports
ISMS officer
Runs the information security management system on behalf of management: risks, reviews and documentation.
On the platform: risk register, treatment plan, versioned documents
ISMS auditors and consultants
Internal and compliance audits, reviews and updating the system after regulatory changes.
On the platform: audit findings as tasks with owners and deadlines
Security analysts
Consult on automated analysis of events and vulnerabilities, and recommend fixes.
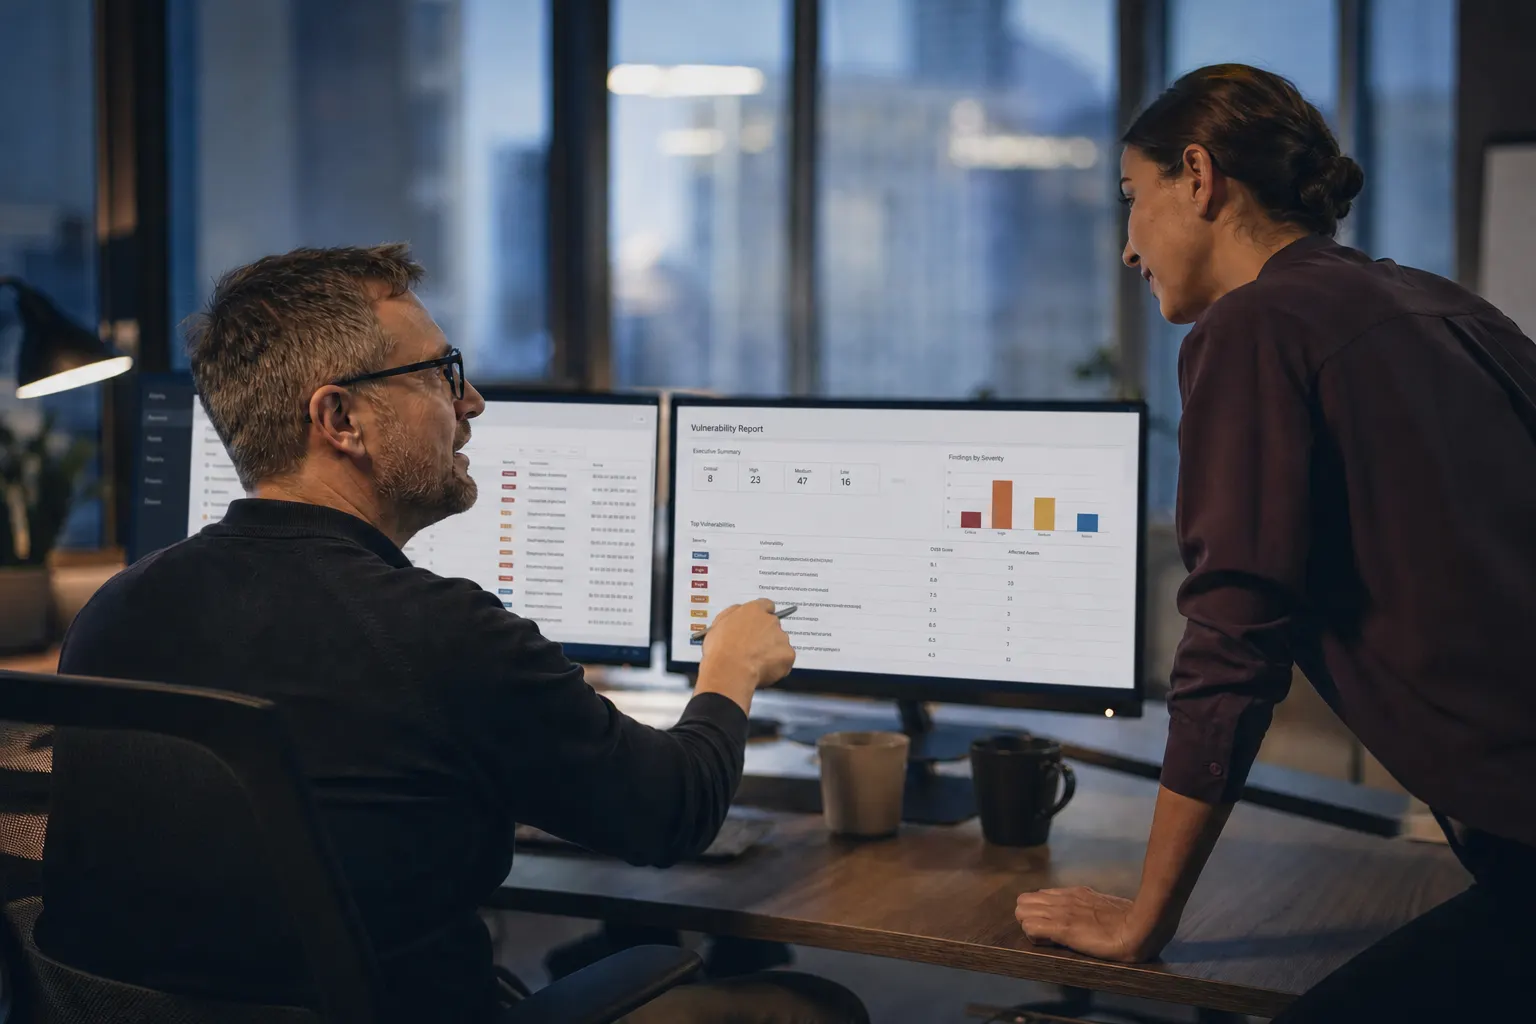
On the platform: console and agents, tests and vulnerabilities
Lawyers and incident handling
Incident classification, reporting, communication and documentation in a crisis.
On the platform: incident register and action history
Trainers
Training, social engineering campaigns and simulator exercises, including annual management training.
On the platform: training paths and campaign results
Who works with whom
Everyone on your side has a counterpart in the FortCyber team. The platform is your shared workspace.
In an incident, lawyers and the incident handling team join in.How we work
Expertise and clearances
- ISO/IEC 27001 lead auditorsRolling out and auditing information security management systems
- KSC auditorsQualified under the 2018 Polish National Cybersecurity System Act (KSC)
- Security clearances“TAJNE” (Polish SECRET), “SECRET UE / EU SECRET”, “NATO SECRET”. Facility security clearance for national, EU, NATO and ESA classified information
- Experienced CISOs and information security officers
- Security testers and a SOC team
- Partner law firm
- Our own information security management system is ISO/IEC 27001 certified
Team certifications
Selected certifications held by our auditors, consultants, pentesters and project managers.
Information security
 Certified Information Systems Security Professional
 Certified Cloud Security Professional
 Certified Information Systems Security Officer
 ISO/IEC 27001 Lead Auditor
 ISO 22301 Lead Auditor, business continuity
- ISMS officer per PN‑ISO/IEC 27001
 IBM QRadar SIEM and Vulnerability Manager
 Check Point Certified Security Administrator
- Check Point Certified Security Expert
Penetration testing
 Offensive Security Certified Professional
 Certified Ethical Hacker
Project and IT management
 PRINCE2 Practitioner and Foundation
 Project Management Professional
 AgilePM Foundation
 ITIL Foundation, IT service management
 Management of Risk
 Management of Portfolios
 Management of Value
 Managing Successful Programmes
Scale and experience
We’ve been building our expertise for 7 years, including on projects for institutions where the stakes are highest.
More than 200 organisations and companies have trusted us, including 110 public bodies and local governments. Over 30 certified auditors and experts work for them, and we have trained more than 20,000 users on our platform.
- NBPNarodowy Bank Polski
A cybersecurity project delivered with NASK.
- PFRPolish Development Fund
A project delivered with the National Cloud Operator.
- PSEPolskie Sieci Elektroenergetyczne
A project delivered with CGI.
Trusted by
See references
How we work
The same principles apply to audits, rollouts and ongoing support.
- We understand first
We learn how your organisation works, its obligations and key processes. Only then do we define the scope of work.
- We speak plainly
Every service ends with a document and a walkthrough of the results. We separate business risk from formalities. If the result is good, we say so.
- We plan for the long term
We plan rollouts around everyday work. We keep registers, reviews and reports going so the system stays up to date.
That’s why our assessment is independent of the provider who runs your systems. We recommend what you need, not what we have to sell.
We share knowledge
We run webinars with experts and write guides for management, IT and ISMS officers.
- Webinar · 12.11.2024Consequences of the NIS2 directive: what you need to know as a board member
- Webinar · 13.12.2024Gap analysis in your organisation: NIS2 directive requirements
- Webinar · 25.02.2025Experience of implementing NIS2 in the Czech Republic and Germany
Meet the team that will run your security
At the meeting:
- you’ll meet the manager and ISMS officer who will work with you
- we’ll show you how we work together on the platform
- we’ll agree where to start in your situation
Incident in progress? Call +48 699 587 010
We’ll get back to you within one working day.